Immediate answer: do not send an OTP, UPI PIN, card PIN, banking password or remote-access permission to a recruiter. Verify the employer before sharing identity documents and provide only fields needed for a stated purpose.
Separate application from onboarding
An early application needs enough information to assess suitability, not full financial credentials. Identity and payroll data may become relevant after a genuine offer and verified onboarding path. A WhatsApp contact asking for Aadhaar, selfie, bank statement and payment in the first conversation is combining risks that should remain separate.
Use a disclosure ladder
- Public profile or résumé with limited contact information.
- Role-specific application through an official channel.
- Interview and confirmation of the legal employer.
- Written offer and verified onboarding contact.
- Minimum identity and payroll information through a secure process.
Each step earns the next; urgency does not replace verification.
Watermarking and redaction
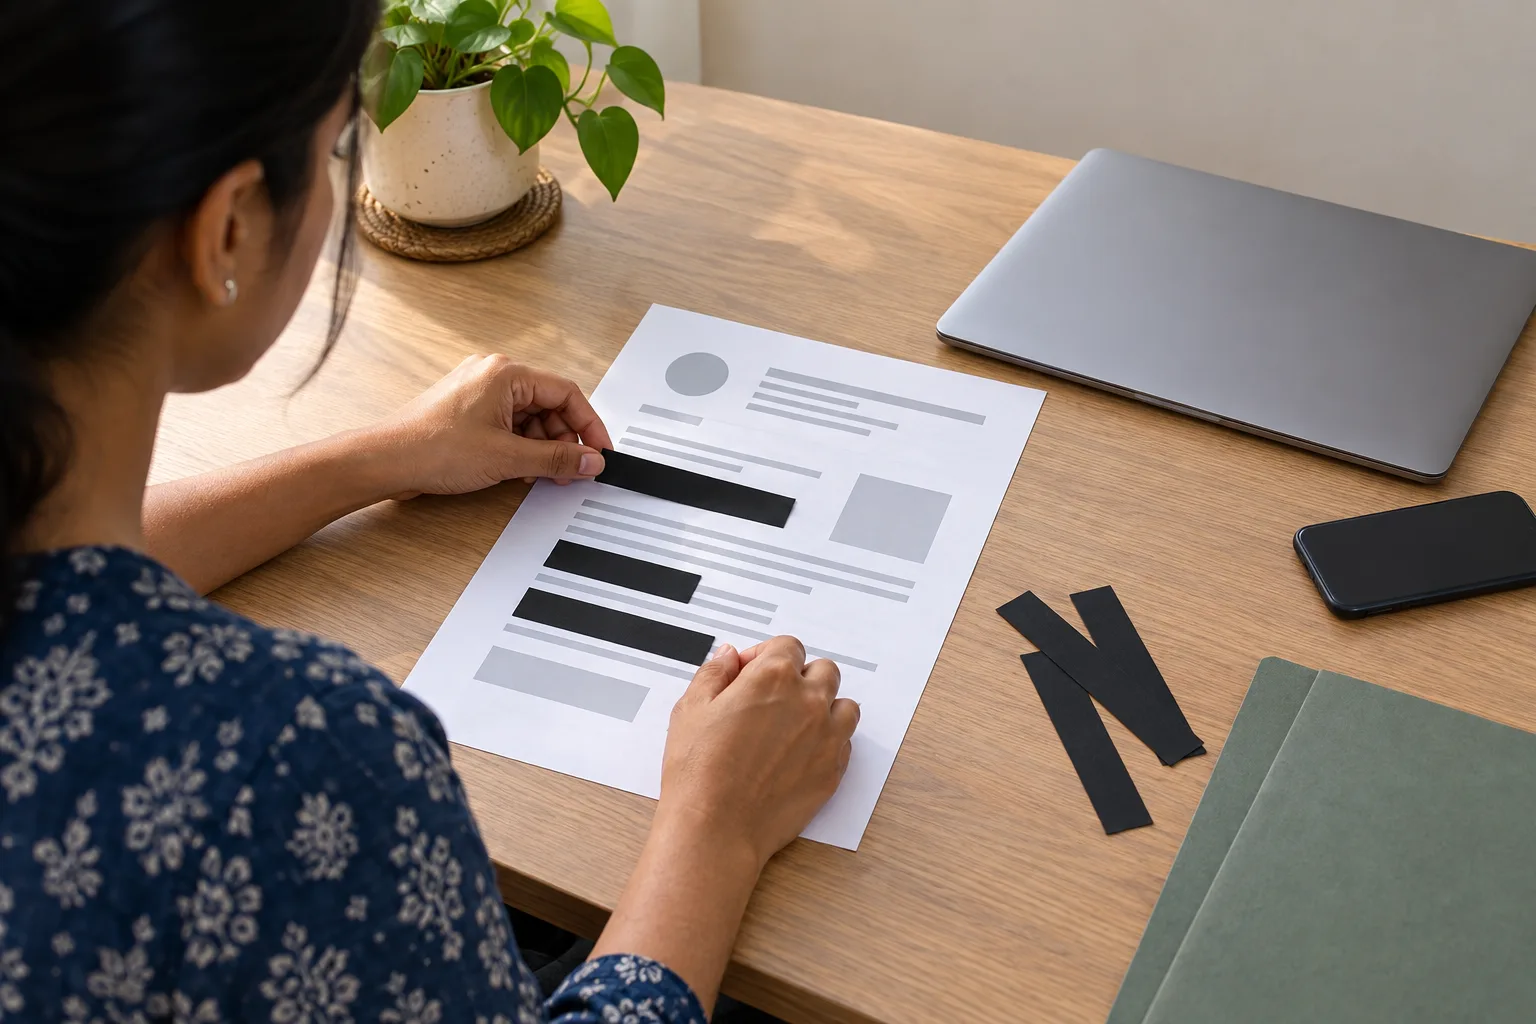
If a document is genuinely required, add recipient, purpose and date and obscure fields that are not necessary. Keep a copy of what you sent. This can reduce casual reuse but is not a guarantee. Never watermark and then send to an unverified person assuming it is safe.
Phone permissions and apps
Do not install an APK from a message or grant accessibility, screen sharing, notification reading or device administration for a job. A recruiter does not need to watch your banking screen. If you already granted access, disconnect, remove suspicious software, review permissions from a trusted device and change exposed credentials.
Scenario: a supposed packing company asks for a selfie holding Aadhaar to issue an ID card before explaining the contract. The order is reversed. First verify the legal employer, role and official process. If that cannot be done, do not send the image.
Build a low-exposure job-search identity
Use a dedicated email address for applications and a résumé that omits unnecessary home address, identity numbers, marital status and financial details. A city and professional contact method are often enough at the early stage. Review cloud-sharing permissions so one résumé link does not expose an entire drive.
Consider whether a public phone number is necessary on every job board. Platform messaging or a dedicated number can reduce spillover, but it does not replace caution. Block and report accounts that move immediately from a vacancy discussion to money, OTPs or intimate personal data.
Document handling after a genuine offer
Confirm which team receives the document, how to upload it and why each field is required. Prefer a secure portal on the employer’s controlled domain to a personal chat. Record the date, recipient and purpose. If instructions suddenly change to a different email or app, re-confirm through the original official channel.
If Aadhaar or bank data was already shared
List exactly which pages or fields were visible and to whom. Change exposed account passwords and alert the relevant bank if banking information or device access was involved. Watch for unexpected authentication, SIM, credit or account messages. Do not pay a stranger to “delete” the files; that is another unverifiable promise.
Data requests that need an immediate refusal
- OTP, UPI PIN, card PIN or banking password.
- Screen sharing while a banking or identity app is open.
- Aadhaar biometric or full document before employer verification.
- Remote-access or sideloaded app installation.
- A selfie or signature whose purpose and retention are unexplained.
FAQ
Does watermarking stop identity theft? No. It can add context but cannot control a malicious recipient.
Can an employer ask for bank data? Payroll details may be needed after verified hiring; timing, recipient and secure method matter.
Should I send a PAN or Aadhaar to get an interview? Ask why it is necessary at that stage and verify the employer independently before any sensitive disclosure.
What if I installed an app? Disconnect, remove it, review permissions and change exposed credentials from a trusted device.
Review your exposure periodically
Keep a private list of job platforms, employers and recruiters that received your résumé or documents. Remove public links when a search ends and revoke sharing permissions that are no longer needed. If a breach notice or suspicious message appears later, this record helps identify what the sender may know and which accounts deserve attention. Do not store the list in a public document containing the same sensitive data you are trying to protect.
Editorial judgment
Job seekers cannot eliminate every data risk, but they can refuse irreversible secrets, delay sensitive disclosure until verification and keep a record of each recipient and purpose. A genuine process should tolerate reasonable questions.
Sources checked
- National Cyber Crime Reporting PortalChecked 23 September 2026
- Ministry of Home Affairs — NCRP and helpline 1930Checked 23 September 2026
Next useful step
Return to Verify an Offer, read the editorial method, or send a documented correction through Contact.